Publication
Critical Infrastructure: It's What's for Dinner
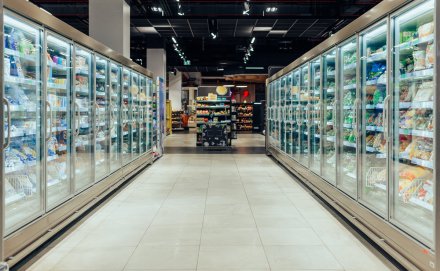
When we think about critical infrastructure, we often picture power plants, water utilities, hospitals, and transportation systems. But what about the grocery store down the street?
Food and agriculture are also part of our nation's critical infrastructure. And a recent cyberattack in France offers a costly reminder that attackers don't necessarily need to steal data or shut down an entire network to cause significant damage. Sometimes, all they need to do is change a temperature.
What Happened in the French Supermarket Cyberattack? When a Few Degrees Become a Multimillion-Dollar Problem
In October 2026, cyberattacks targeted refrigeration systems at hundreds of French supermarkets, including locations operated by Intermarché, Coopérative U, and other major grocery chains.
Attackers remotely manipulated refrigeration controls, reportedly raising temperatures to as high as 122°F (50°C) and altering defrost settings. The result was widespread food spoilage, discarded inventory, interrupted operations, and substantial financial losses.
French officials reported that approximately 700 supermarkets were affected. Investigators also examined reports of equipment damage and fires.
What makes this incident particularly concerning is that the attackers weren't simply disrupting computers. They were manipulating technology responsible for maintaining a critical physical process: keeping food at safe temperatures.
The consequences extended beyond the affected equipment. Grocery stores lost inventory, employees had to respond to the damage, and food distribution and replenishment operations faced additional pressure.
Authorities opened an investigation, and questions remained about who was responsible and precisely how the systems were compromised. France's cybersecurity agency identified compromises involving remote refrigeration controllers, including older equipment that was no longer receiving security updates.
The larger lesson is relevant far beyond grocery stores.
What Is Operational Technology (OT), and Why Is It a Target?
Consider how many essential services rely on operational technology (OT), the equipment and software that monitor or control physical processes.
- Water utilities depend on systems that regulate chemical levels and pumping operations.
- Manufacturers rely on automated production equipment.
- Hospitals use connected systems to support critical facilities and patient care.
- Food distributors depend on refrigeration, environmental controls, and transportation logistics.
In each of these environments, a cyberattack could potentially shut down a process, alter operating settings, corrupt information, or undermine confidence that equipment is functioning safely.
And as organizations increasingly connect operational technology to business networks, vendors, and remote monitoring services, the potential pathways for attackers expand.
An employee clicking a phishing email, for example, should not give an attacker a direct route to equipment controlling critical operations.
That is why critical operational systems need additional layers of protection, including:
- Network segmentation
- Restricted access
- Continuous monitoring
- Careful management of vendor connections
The goal is not simply to keep attackers out. It is also to limit what they can reach and what they can change if an initial defense fails.
Four Questions Every Organization Should Be Asking About Critical Infrastructure Security
The French supermarket incident reinforces a fundamental principle of cybersecurity resilience: organizations must understand their most critical services before they can effectively protect them.
Whether you operate a utility, hospital, manufacturing facility, food distributor, or local government, leadership should be asking four questions.
1. What are our most critical services and operations?
Identify the processes your organization absolutely depends on to function. Then determine which technologies, vendors, equipment, and personnel support those services.
Not every system carries the same operational risk. Protecting a system that controls a critical physical process may require different safeguards than protecting an ordinary office application.
2. What could an attacker actually do to those services?
Don't limit the conversation to ransomware or stolen information.
Could someone:
- Change a temperature, pressure, chemical level, production setting, or operating schedule?
- Disable alarms or manipulate monitoring data?
- Make a system appear to be operating normally when it isn't?
Understanding these scenarios helps organizations identify risks that traditional IT-focused assessments may overlook.
3. How are we protecting and monitoring those systems?
Review how operational technology connects to the broader network, the internet, and third-party vendors.
- Are critical systems appropriately segmented?
- Is remote access restricted and monitored?
- Are unsupported devices creating unnecessary exposure?
- Can operators independently detect unusual changes to important settings?
These safeguards can reduce the likelihood that a single compromised account, vulnerable device, or vendor connection becomes a much larger operational crisis.
4. What happens if those protections fail?
This may be the most important question of all.
If critical operational technology becomes unavailable or cannot be trusted, what happens next?
- Do employees know when to shut down a process?
- Can operations continue safely through alternative or manual procedures?
- Who makes those decisions?
- How will IT, operational leadership, executives, legal counsel, and external partners coordinate the response?
How will the organization safely restore services when the incident is contained? Those answers should not be developed for the first time during a cyberattack.
Why Cyber Resilience Matters as Much as Cyber Protection
Strong cybersecurity controls reduce risk, but no organization can guarantee that every attack will be prevented.
That is why operational resilience must be part of the conversation from the beginning.
- A cybersecurity incident response plan that establishes leadership responsibilities, escalation procedures, internal and external communications, and coordination across operational and technical teams.
- A disaster recovery plan that identifies technology dependencies, restoration priorities, and procedures for returning systems to service safely.
- Business continuity plans and downtime procedures should address how essential operations will continue, or be safely suspended, while recovery is underway.
Most importantly, these plans need to be practiced. Tabletop exercises involving IT, operations, leadership, legal, and relevant vendors allow organizations to test their assumptions before an actual incident. They can reveal gaps in decision-making, communications, monitoring, and restoration that might otherwise go unnoticed.
The French supermarket incident offers a reminder that cyberattacks against critical infrastructure can cause real-world damage without involving a traditional ransomware attack.
And the consequences can extend from a compromised controller to damaged inventory, interrupted services, financial losses, and communities that depend on those operations.
You cannot protect what you haven't identified as critical, and you cannot be resilient if you haven't planned for what happens when it fails.
As we recognize Critical Infrastructure Security and Resilience Month, that is a lesson worth bringing to every leadership table, including the dinner table.
How Prepared Is Your Organization?
Ice Miller's Tech, Privacy & Cyber Risk team helps organizations assess critical operations, build incident response plans and run tabletop exercises. Contact our team to get started.
This publication is intended for general information purposes only and does not and is not intended to constitute legal advice. The reader should consult with legal counsel to determine how laws or decisions discussed herein apply to the reader's specific circumstances.